Authorized Dealer
Keep your data safe with the 4TB Aegis Secure Key USB-A 3.2 Gen 1 Flash Drive from Apricorn. This USB-A 3.2 Gen 1 (3.1 Gen 1/3.0) drive features a storage capacity of up to 4TB, read speeds of up to 195 MB/s, write…
Product highlights and buying context
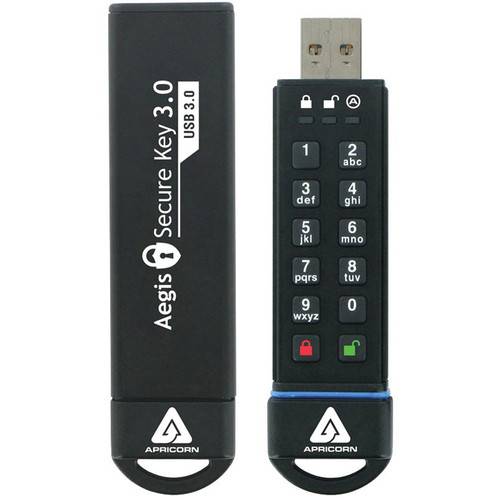
Keep your data safe with the 4TB Aegis Secure Key USB-A 3.2 Gen 1 Flash Drive from Apricorn. This USB-A 3.2 Gen 1 (3.1 Gen 1/3.0) drive features a storage capacity of up to 4TB, read speeds of up to 195 MB/s, write speeds of up to 162 MB/s, and is protected with 256-bit AES military grade hardware encryption and a 7- to 16-digit PIN. Its drive reset feature clears pins, destroys data, and generates a new random encryption key for reuse.
The Aegis' extruded aluminum chassis is crush resistant up to 6500 lb and tamper evident while an epoxy compound prevents the removal of internal circuitry without causing permanent damage. It automatically locks upon removal from the computer or loss of power, or after a pre-programmed period of inactivity.
To prevent the access of unauthorized individuals with keyloggers or brute force attacks, the Aegis has its own wear-resistant keypad for entry. The Brute Force Hack Defense Mechanism deletes the encryption key and all data if the incorrect PIN is entered up to a total of 20 consecutive times.
The heart and soul of every Apricorn Secure Device, AegisWare is their patent-protected firmware combined with the industry's most advanced feature set.
Meets the U.S. government standards for information technology and computer security. NIST FIPS 140 is the cryptography standard program required by the US federal government for protection of sensitive data. The Aegis Secure Key's FIPS 140-2 validation covers 11 areas of its cryptographic security system, including physical security, cryptographic key management and design integrity. Available in four levels, the Aegis Secure Key's FIPS 140-2 Level 3 validation encompasses both the Aegis Secure Key's physical tamper-resistant features as well as its identity-based authentication. Tested and validated by the National Institute of Standards and Technology (NIST) for use by the Federal governments of the USA, Canada and others, the Aegis Secure Key 3 is based on Apricorn's FIPS 140-2 Level 3 validated encryption module as indicated by certificate #2834. The Secure Key's security policy is located on the NIST site at the following link. The epoxy coated boundary includes all encryption functions and all Critical Security Parameters (CSPs) such as PIN storage, encryption key generation and storage, random number and seed generators, all firmware storage, and device storage. The FIPS module is a complete encryption system, and all CSPs never leave the boundary and are never shared with a host system.
Create custom profiles and mass configure multiple devices in a matter of seconds using the Aegis Configurator, a Windows-based app that can be used to set up multiple devices simultaneously. To configure an expanded number of devices, use the Powered Aegis Configurator Hub bundle.
The Aegis Secure Key USB flash drive supports independent Admin and User PINs. The Admin (Device Configuration) Mode controls the universal programmable settings of the device and can only be accessed with the Admin PIN. The User Access Mode is limited to basic external drive functions like read /write, unlock / lock, etc. The data on the drive can also be accessed with the admin PIN in the User mode.
The drive is unlocked by entering a PIN on its keypad and not the host computer's keyboard. Until the device is unlocked via its keypad, it remains invisible to the host. The embedded keypad circumvents all hardware and software key logging attempts to capture passwords by excluding the host system from the authentication process. Polymer-coated buttons are wear-resistant and designed to not reveal most commonly used buttons.
A unique PIN must be established at time of setup, which eliminates factory default PIN vulnerability. Out of the box, there are no factory pre-set default PINs. In order to set up and use the drive, a unique PIN must first be established by the Admin from within the Admin Mode.
The Admin can program the device at setup to require the user to establish a unique PIN. Once a device is configured by the Admin, it can then be deployed in a state of USER FORCED ENROLLMENT in which the User must first establish his or her own User PIN before the drive can be accessed or used.
In the event that a User PIN is forgotten, Recovery PINs can be programmed into the device to permit access to the drive's data by creating a new state of User Forced Enrollment while the Admin PIN and the drive's data remain intact. Once a replacement User PIN is generated, access to the drive is restored for the user.
The two Read-Only modes are as follows: Universal Read Only is set by the admin from within the admin mode and can't be modified or disabled by anyone but the admin. The second read-only mode can be set and disabled by a user, but can also be enabled or disabled by the admin as well.
The Admin designates minimum and maximum PIN lengths (between 7 and 16 characters). The longer the PIN, the more secure the data on the device becomes. For example, the odds of brute force success go from 1/10,000,000 with a 7-digit PIN to 1/100,000,000 with an 8 digit PIN. In cases where the User sets up his or her own PIN from User Forced Enrollment, the Admin can set an enhanced User password length requirement as part of the overall security policy.
Select the number of consecutive invalid PIN attempts permitted (4-20) before crypto-erase. All Aegis Secure USB Flash Drives are unlocked (authenticated) by entering a PIN on their own onboard keypad. Since the PIN is not entered using the host computer's keyboard, they are not vulnerable to software or hardware-based key-loggers or software-based brute force attacks. However, if the device comes under a physical brute force attack, your data is protected with a programmable "Brute Force Hack Defense Mechanism" which, if the programmed number (between 4 and 20) of consecutive incorrect password entries has been attempted, the device will delete its own encryption key and destroy the ability to decrypt its stored data.
All Aegis Secure Drives will automatically lock once disconnected from a computer's USB port or the power to that USB port is interrupted, or after a pre-programmed period of inactivity.
The override allows the drive to remain unlocked during USB port renumeration (virtual machine, remote boot). It's designated for specific cases in which the key needs to remain unlocked through USB port re-enumeration such as during reboot, or passing through a virtual machine.
All Apricorn devices can be reset and redeployed over and over. The Drive reset clears both the User and Admin PINs, destroys the data, creates a new randomly generated encryption key and allows the drive to be reused repeatedly, with an infinite number of randomly generated encryption keys, allowing the admin and or user to reset the drive as often as is needed.
When programmed and activated, the Self-Destruct PIN performs a crypto-erase and becomes the new access PIN. It's the last line of defense for data security when the device's physical security is at risk. The Self-Destruct PIN defends against these physically compromising situations by erasing the key's contents, leaving it in normal working order appearing yet to be deployed.
Visually confirms successful button presses via the device's LEDs.
A dust- and water-resistant durable aluminum housing goes well beyond encryption. Tough enough to go anywhere, the Aegis Secure Key's resilient design makes it perfect for travel and field applications. With its rugged, extruded aluminum crush-resistant casing, the Aegis Secure Key is tamper evident and well-protected against physical damage.
Additional Details
Loading…
